Can a Condominium Guardhouse Keep Your IC? What a JMB May Collect.
QUESTION ANSWEREDThe guardhouse is holding visitors' identity cards and writing their details in a book: what is the building actually allowed to ask for, and what happens to the record?
A condominium guardhouse may ask a visitor to identify himself, and may not keep his identity card. The National Registration Department stated in June 2025 that security guards have no authority to request, hold or scan a MyKad. Unreasonably detaining another person’s card is separately a criminal offence. By-law 17(1) of the prescribed strata by-laws allows the first and never the second.
- 01Five categories of officer may demand an identity card, and a security guard is not oneREGULATION 7
- 02Unreasonably detaining another person’s card carries up to three years or RM20,000REGULATIONS 8A + 25
- 03By-law 17(1) lets management require a person to identify himself, not to surrender a documentIDENTIFY
- 04A person who refuses may be asked to leave, unless he is a proprietorBY-LAW 17(2)
- 05No Malaysian rule states how long a gate record may be keptUNSET
Can a condominium guardhouse keep your IC?
No. On 10 June 2025 the National Registration Department put it plainly: “Security guards do not have the authority or right to request, hold or scan Malaysian identity cards (MyKad)”. It went further — “Any action by security guards to request or keep identity cards is against the law”.
Only five categories of officer may demand and inspect a card under Regulation 7(1) of the National Registration Regulations 1990: NRD, police, Customs, military personnel on duty, and civil servants authorised by the director-general. A guardhouse is not an arm of government.
Holding a card is the sharper end. Unreasonably detaining another person’s identity card is a criminal offence under Regulation 8A, punishable under Regulation 25 by up to three years, a fine up to RM20,000, or both. Regulation 6 explains why: custody is the holder’s own duty, and does not transfer to a counter.
What may management actually require at the gate?
Management may require a name. By-law 17(1) of the Third Schedule to the Strata Management (Maintenance and Management) Regulations 2015 says management “may require any person on the common property to identify himself for security purposes”. Read the verb: it authorises requiring identification, not taking, scanning or retaining a document, and no other prescribed by-law supplies what it leaves out.
The sanction is equally narrow. By-law 17(2) reaches a person “who refuses to comply with paragraph 17(1) of these by-laws and who is not a proprietor”, who may be required to leave immediately. A visitor can be turned away; an owner cannot — a line most gate procedures ignore.
Either way the gate is the building’s own job: section 21(1)(a) of the Strata Management Act 2013 puts a joint management body under a duty to keep the common property “in a state of good and serviceable repair”. The guard company performs the procedure; it does not own it.
May the guardhouse scan or photograph a MyKad?
The National Registration Department addressed scanning separately and said no: “using electronic devices to scan MyKad data is also not allowed as this is subject to the Personal Data Protection Act 2010”. Two objections in one sentence: the scanning, and everything that follows once an image exists.
How far the PDPA reaches a building is unsettled: section 2(1) applies it to “any personal data in respect of commercial transactions”, and whether a management body running a gate sits inside that phrase is resolved nowhere we have found — the open question set out in what a JMB inherits at developer handover.
What may the guardhouse record instead?
A lawful alternative to holding a card has been published since 2007. A Ministry of Home Affairs circular that year told security companies “to immediately cease from holding on to the identification documents of visitors”, and allowed them only to ask for a visitor’s identification document, “record their identity and return it to the visitor immediately”.
The circular and the 2025 statement do not agree on the asking — one permits it, the department says a guard has no authority — so the safe route is the part both leave standing: a document produced voluntarily, its particulars written down, and handed straight back.
The record is where the duty moves from the guard to the building. Where the Act applies, section 7(1) requires the building to inform the visitor “by written notice” — not a verbal assurance from whoever is on shift. Section 7(1)(g) names the part every guardhouse omits: the notice must state “whether it is obligatory or voluntary for the data subject to supply the personal data”.
| Step | Permitted? | Where it comes from |
|---|---|---|
| Require identification | Ask who the person is, for security purposes | By-law 17(1) |
| Sight a document | Only as offered, never demanded | Circular 2007; NRD, 2025 |
| Record the particulars | Write the identity down, return it immediately | The same circular |
| Hold the card | Not permitted | Regulations 8A and 25 |
| Scan or photograph it | Stated as not allowed | NRD, 10 June 2025 |
| Turn away a refusal | A visitor, yes. A proprietor, no | By-law 17(2) |
Who may read the visitor log, and how long may it be kept?
The visitor may read his own entry: under the access principle a person “shall be given access to his personal data held by a data user”. Inside the building, reading is for named accounts, not one login shared by every shift. On how long, no Malaysian rule names a number, so the building sets the period and writes it down.
A gate log names people and the homes they went to. The security principle requires practical steps against “loss, misuse, modification, unauthorized or accidental access or disclosure”, and names among its factors “the place or location where the personal data is stored”. An open book readable by the next person in the queue fails on its face. What may be released about other people is the harder half, answered for recordings in what a JMB may release from CCTV footage.
Section 10(1) says personal data “shall not be kept longer than is necessary for the fulfilment of that purpose”, and the Commissioner’s Storage Standard requires deletion once it is no longer processed — covering “electronic and non-electronic handling”, so the paper book is inside it, which leaves the period the same unset question as for footage.
Whose record is it when the guard company changes?
The visitor management system is usually the guard company’s tablet on its own subscription, or a vendor cloud account opened in a manager’s name. The contract is re-tendered, and every record of who entered the building leaves with the outgoing party — or worse, stays with them.
The PDPA contemplates the arrangement. Where a processor handles data on the building’s behalf, the building must ensure it “provides sufficient guarantees in respect of the technical and organizational security measures governing the processing to be carried out”. Section 10(2) then requires reasonable steps to see data destroyed or permanently deleted once no longer required — which somebody must perform, on a system somebody else administers. Both are contract clauses before they are settings — what the guarding contract should oblige and what a maintenance contract must say about lock-in.
What can a committee settle this week?
Settling a guardhouse’s visitor policy needs no consultant. Walk to the guardhouse at a busy hour and look at what is on the counter and in the drawer. Each line below is either already true, or it is an action.
- N01No identity card is held at the counter at any point in a shiftOBSERVED
- N02A written notice states the purpose, and whether giving details is obligatoryPOSTED
- N03The record lives somewhere named: a book, a terminal, an accountLOCATED
- N04Accounts that can read, export or delete the log are listed, none sharedNAMED
- N05A retention period is written down, with something that performs the deletionDATED
- N06The contract says what happens to the records when the contractor changesCONTRACTED
Where the system was inherited rather than bought, an as-found survey establishes the account behind it first.
Why is the gate one layer rather than one device?
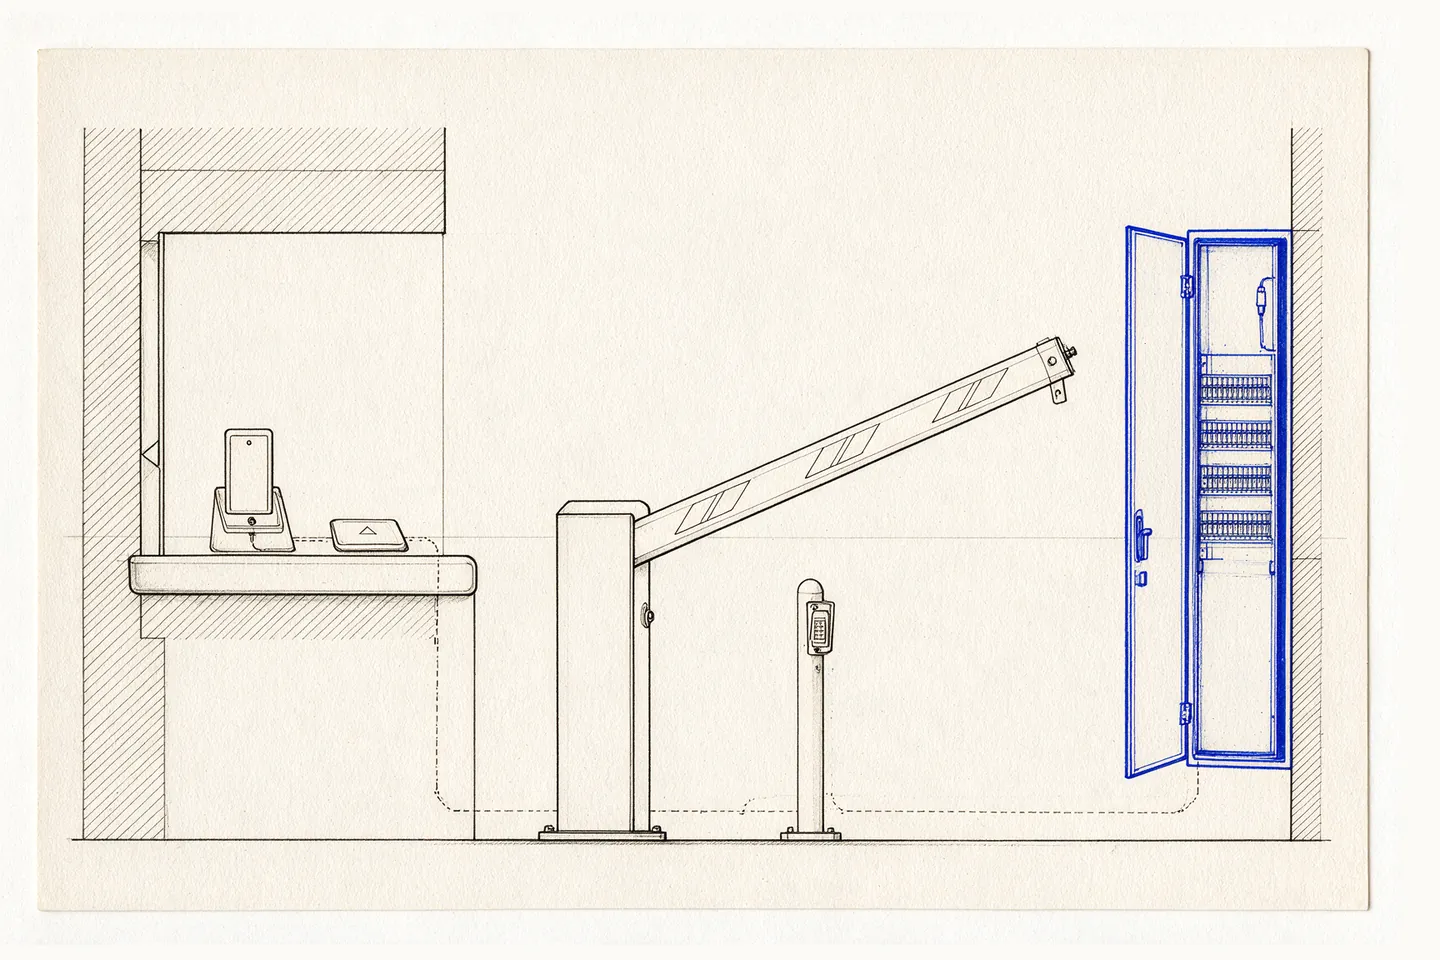
A gate is a chain — intercom, barrier, camera, and the terminal that writes the record — and splitting it between a guard company, a barrier supplier and an app vendor is what goes wrong when a building’s ELV systems are split.
Occhio Tec is an Extra Low Voltage contractor established in 2010, working mainly on condominiums in Mont Kiara, Bangsar and KLCC. It designs, installs and maintains CCTV, access control, video intercom, structured networking and perimeter intrusion, and takes over systems another contractor installed. Where a gate record lives cannot be read off a drawing: request a site survey or message +60 11-6494 4931.
Questions about what a condominium guardhouse may collect
Q-01The guard says holding the IC is company policy. Can we carry on?
No, and the policy is the problem. The National Registration Department’s position is that any action by security guards to request or keep identity cards is against the law, and unreasonably detaining another person’s card carries up to three years or RM20,000. The 2007 circular leaves only the narrow route: record the particulars, hand the document straight back.
Q-02Can we refuse entry to someone who will not identify himself?
A visitor, yes. By-law 17(2) reaches a person who refuses to comply with by-law 17(1) and who is not a proprietor, who may be required to leave immediately. The exclusion of proprietors is express, so the same refusal from an owner is handled differently.
Q-03A resident wants the gate log showing who visited them. Must we give it?
Their own data, largely yes: the access principle says a person shall be given access to his personal data held by a data user. Entries naming other visitors are the harder half, following the reasoning in footage showing other people. Decide it once, in writing.